





HIPAA Compliance & Data Security
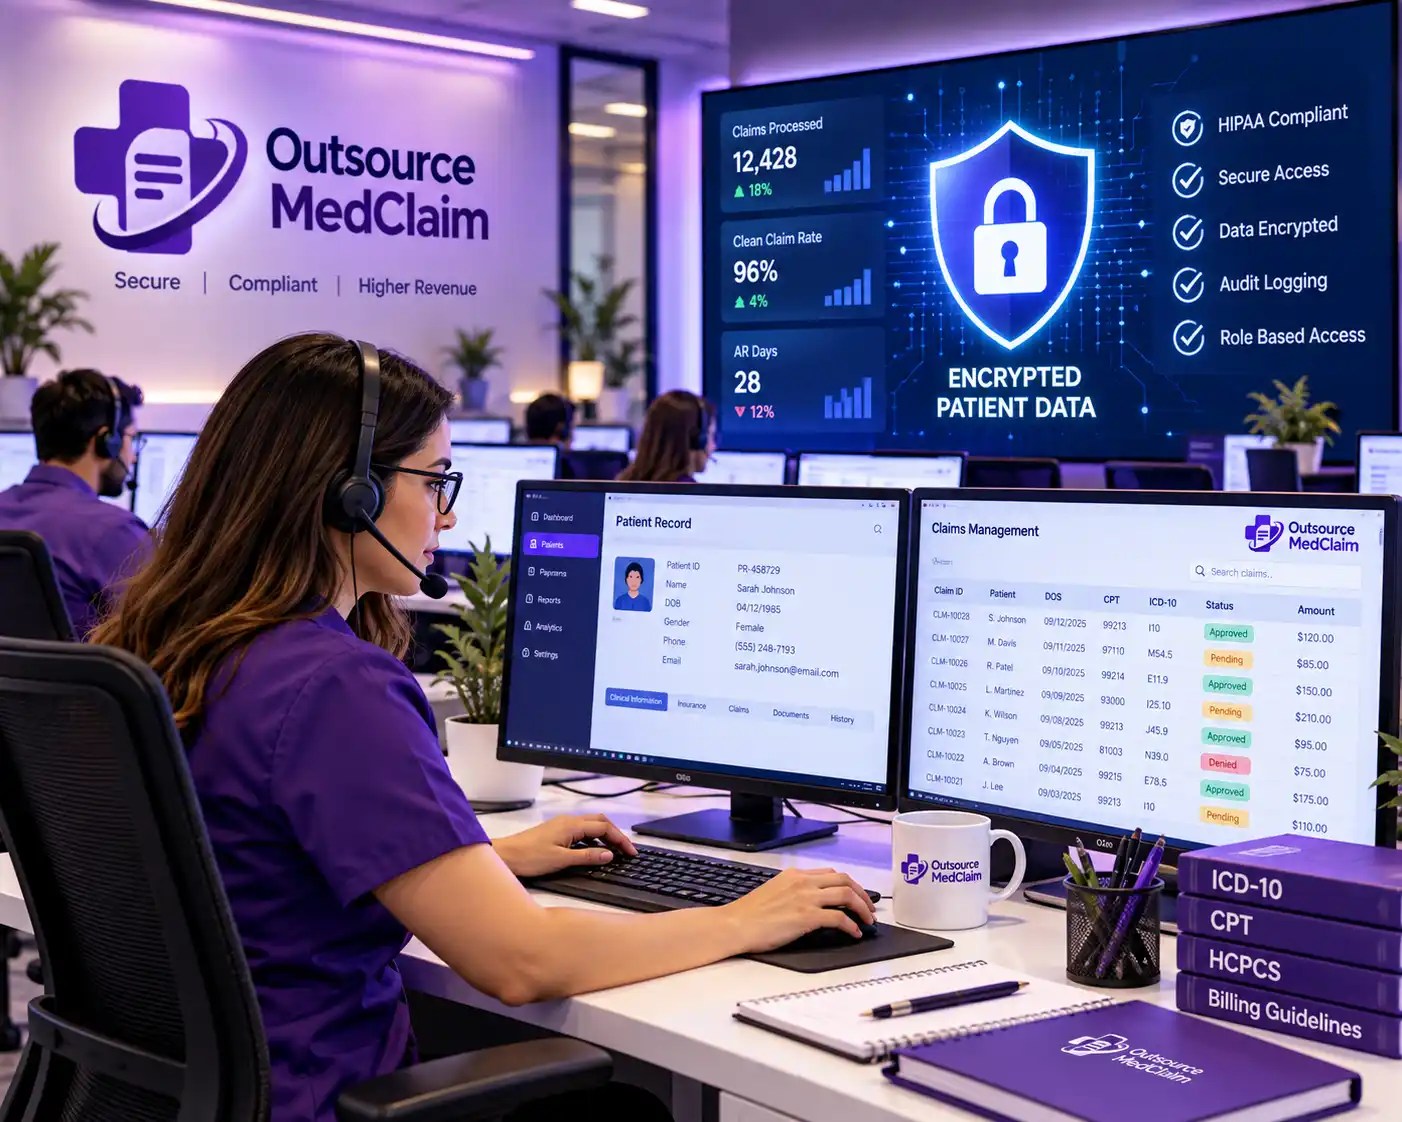
At Outsource MedClaim, we recognize that data security is just as critical to healthcare providers as clinical accuracy. As your Business Associate, we are committed to the highest standards of the Health Insurance Portability and Accountability Act (HIPAA) and the HITECH Act. Our compliance framework is designed to protect Protected Health Information (PHI) at every stage of our revenue cycle management, medical coding, and medical billing services, from initial intake to final payer remittance.
We don't just follow the rules; we build a culture of security around your practice's financial and patient data.
Our Three-Pillar Security Framework
In alignment with the 2026 HIPAA Security Rule updates, we implement a robust triad of safeguards:
 01
Administrative Safeguards
The foundation of our security program lies in our rigorous internal policies:
Dedicated Security Officer: We have an appointed official responsible for overseeing all compliance efforts and acting as your point of contact for security audits.
Annual Risk Analysis: We conduct thorough assessments of our systems to identify and mitigate potential vulnerabilities before they can be exploited.
Sanction Policy: We hold our workforce accountable with strict disciplinary procedures for any non-compliance with our security protocols.
72-Hour Recovery Requirement: Our contingency plans are tested to ensure critical billing systems can be restored within 72 hours of any disruptive incident.
 02
Physical Safeguards
We protect the physical infrastructure that houses your sensitive information:
Facility Access Controls: Our operational centers use biometric and keycard access to prevent unauthorized entry into data-processing areas.
Workstation Security: Every workstation is positioned to prevent unauthorized viewing and is configured with automatic logoff timers.
No-Data-Capture Policy: Our billing specialists work in "clean-room" environments where recording devices, USB drives, and unauthorized personal electronics are strictly prohibited.
 03
Technical Safeguards
We utilize industry-leading technology to defend your ePHI:
Mandatory Multi-Factor Authentication (MFA): Access to any system containing patient data (Epic, Cerner, athenahealth) requires MFA—no exceptions.
AES-256 Encryption: All data is encrypted at rest and during transmission to payers and clearinghouses.
Role-Based Access Control (RBAC): Staff members can only see the specific data required for their job function (the "Minimum Necessary" standard).
Continuous Audit Logging: Every system interaction is logged and reviewed regularly to detect and report anomalous activity.
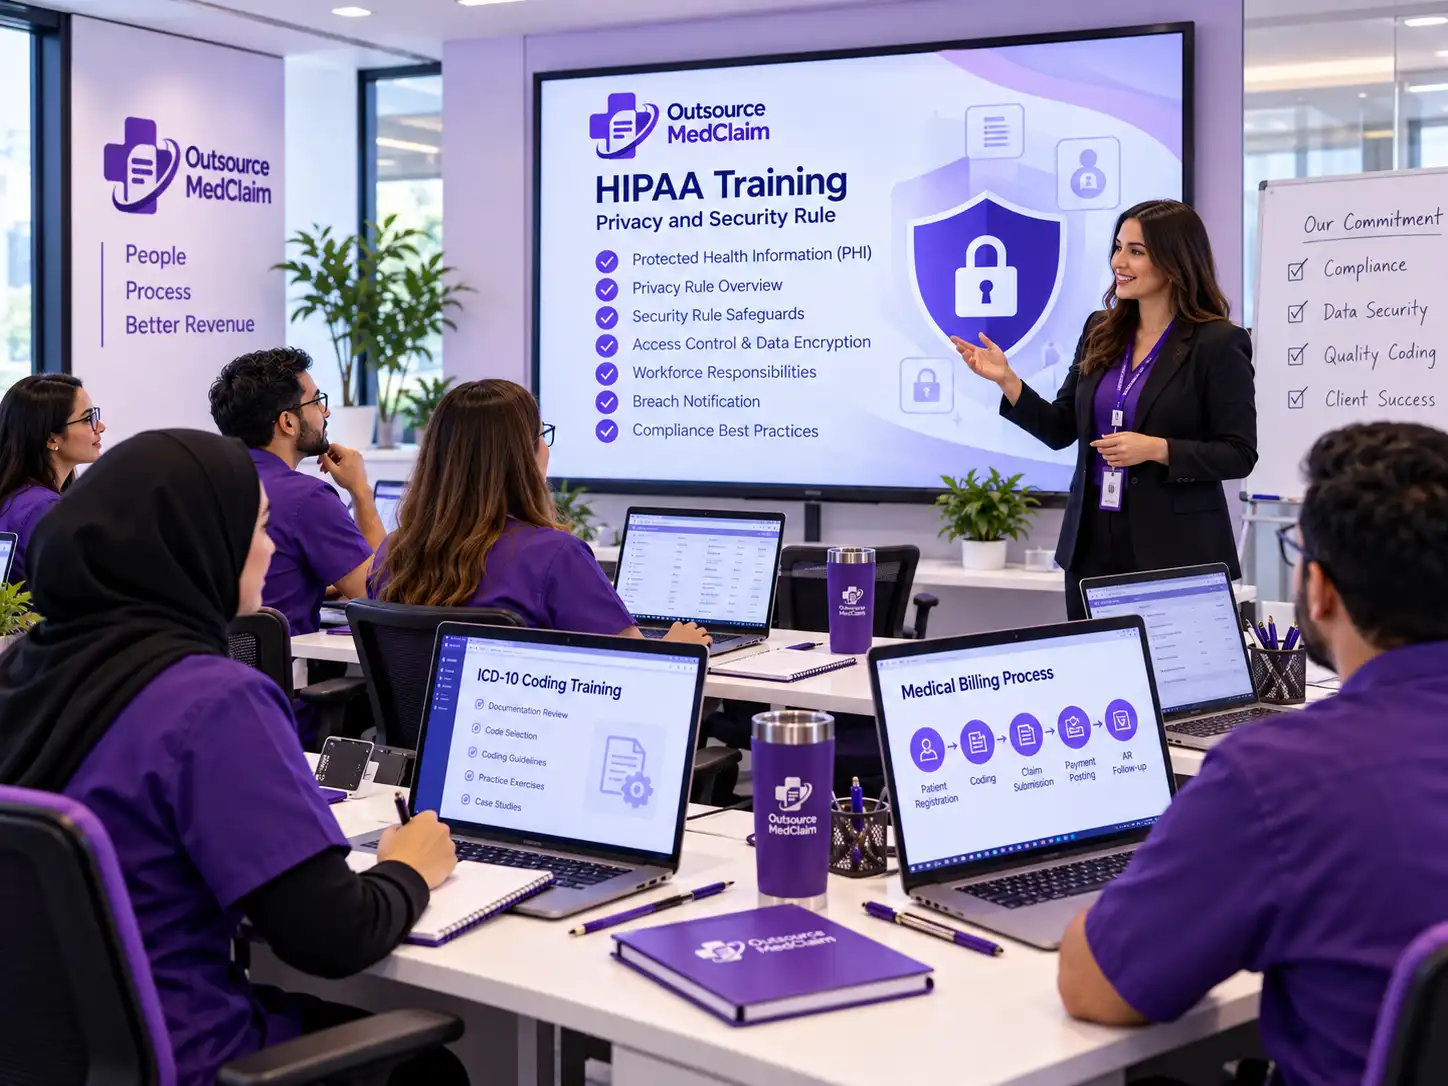
Specialist VMA & Billing Staff Training
A security system is only as strong as the people operating it. At Outsource MedClaim, every employee, from our bilingual Virtual Medical Assistants to our AAPC-certified coders, undergoes:
Our Promise to Your Practice
When you partner with Outsource MedClaim, you receive the protection of a formal Business Associate Agreement (BAA) in compliance with our Privacy Policy. Contact our team to request a signed BAA prior to initiating any service. This document legally binds us to:
FAQ’s
We use secure, encrypted tunnels (VPNs) to connect to your existing EHR. Data never resides on our local servers unless explicitly required for a specific, secure workflow.
Yes. We maintain a documented Incident Response Plan and conduct annual tabletop exercises to ensure our team is ready to contain and report any potential threats immediately.